
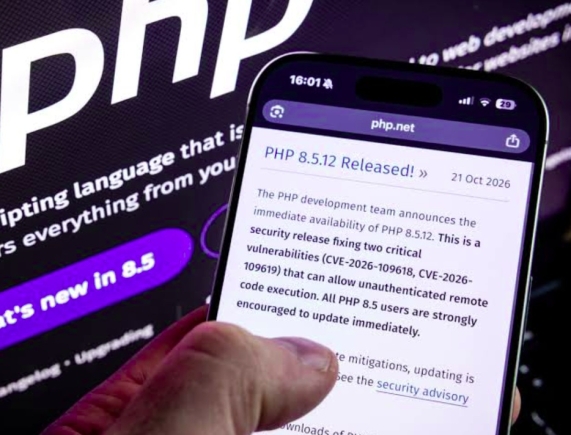
The Cyber Security Authority (CSA) and the National Information Technology Agency (NITA) have jointly issued a public security alert warning of two critical vulnerabilities in PHP, a programming language widely used to power websites and online services in Ghana.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619 and collectively known as “PHP2Shell,” could enable attackers to take control of vulnerable servers without requiring a username or password. Successful attacks could lead to the exposure of sensitive data, disruption of online services and further compromises of an organisation’s network. The warning is directed at government institutions, businesses, website owners, hosting providers and operators of critical information infrastructure.
Organisations urged to install security updates
The agencies disclosed that the PHP Project had released security fixes in versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Organisations have been urged to immediately upgrade to the appropriate patched version, a later supported release or a vendor-provided package confirmed to address the vulnerabilities.
The authorities also emphasised that updating website themes or plugins alone would not eliminate the risks, as the flaws affect the underlying PHP software. Organisations must therefore ensure that their PHP installations are updated to a secure version to mitigate potential attacks.
Immediate actions
The agencies outlined five urgent measures for organisations affected by the vulnerability. First, they advised organisations to identify all websites, web applications and servers running PHP, including those managed by third-party providers, while prioritising internet-facing systems and critical public services. Second, they urged the immediate installation of security updates in accordance with vendor guidance, including restarting affected services where necessary and verifying that the patches had been successfully applied.
Where updates could not be implemented promptly, organisations were advised to temporarily take vulnerable services offline until they could be secured. Third, organisations were instructed to investigate potential compromises by examining system logs, unusual processes, unexpected administrator accounts and unauthorised modifications to website files.
Any suspected compromised systems should be isolated, with evidence preserved for further investigation. Finally, organisations were directed to obtain written confirmation from hosting providers, developers and system administrators that all affected systems had been identified and patched.
7-Day deadline for government institutions
Heads of government institutions have been instructed to ensure their ICT teams and service providers take immediate action to address the identified vulnerabilities. The National Information Technology Agency (NITA) will provide technical support for government digital assets and services, while the Cyber Security Authority (CSA) will oversee cybersecurity incident reporting and response efforts.
Institutions are also required to maintain updated inventories of their digital assets and designate responsible officials to facilitate remediation and coordination in line with NITA’s Government Digital Assurance Programme. All institutions must implement corrective measures within seven days and submit reports on actions taken to both the CSA and NITA.
Advice to the public
The public has been urged to be cautious of messages asking them to download a “PHP security update,” disclose passwords or provide payment details. Website owners should obtain updates through official software sources or verified service providers. Cybersecurity incidents or suspected compromises can be reported to the CSA by calling or sending an SMS to 292, or by email at report@csa.gov.gh. Government digital services coordination and GovDAP enquiries can be directed to NITA by email at govdap@nita.gov.gh or by telephone on 055 249 9661. The agencies urged all affected organisations to treat the alert as urgent and act immediately.

